How to Create a Strong Password for Your Casino Account
Most people use terrible passwords for their casino accounts. That is how accounts get drained. Here is my take on what a strong password actually looks like and why the casino requirements are not enough.
The casino account password you use is almost certainly not strong enough. My thesis: the default password requirements at most casino sites are insufficient to protect an account that might hold thousands of dollars, and players should exceed those requirements significantly because the attackers targeting casino accounts are better resourced than most people realize.
Casino accounts are juicy targets. They hold real money. They are often linked to payment methods (cards, e-wallets, bank accounts) that can be cashed out. They are accessed from mobile apps where password hygiene is worse. They have weak-by-default security requirements because every casino operator is optimizing for sign-up conversion, not for account security. The result is a system where attackers routinely drain accounts and the victim does not know until they try to withdraw and find the account empty.
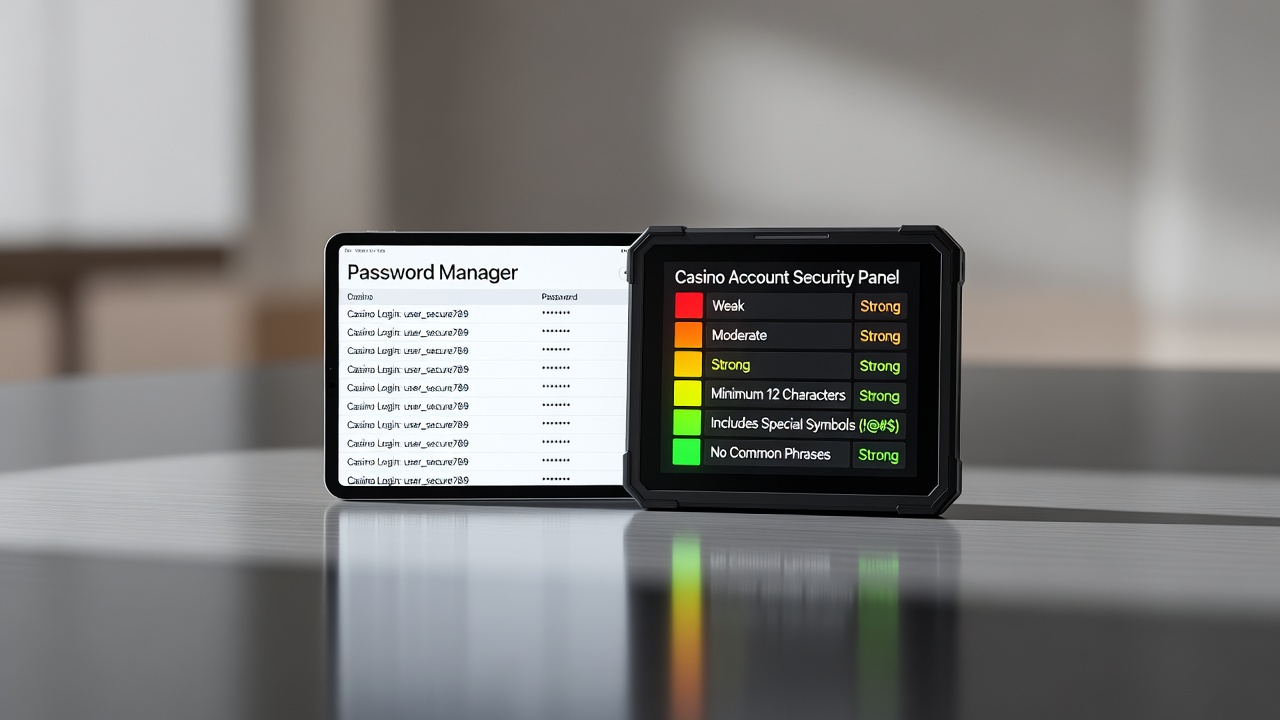
Here is what a strong password looks like. Minimum 16 characters, ideally 20 or more. Mixed upper and lower case. Numbers and symbols. Not based on any word in any language, not based on your name, birthday, or any personal detail that could be discovered through social engineering or data breach leaks. Generated by a password manager, not invented in your head. Unique to the casino account. Not shared with any other site.
Why this matters
The counterargument is: come on, it is a casino account, it is not my bank. Overkill. Any login will be fine. This is wrong, and it is wrong in a specific way. Casino accounts are in fact being systematically attacked right now by credential-stuffing botnets that cycle through username-password pairs leaked from other breaches. If you use the same password at your casino that you used at a site that got breached in 2019 or 2021 or 2023, your casino account is on a target list. The attackers have automation. They try thousands of accounts per hour. If one hits, they drain it.
A password manager is not optional. I will state that directly. Bitwarden, 1Password, Dashlane, or even the built-in iCloud Keychain or Google Password Manager. Any of them is sufficient. The key is that you have a unique password for every account, and the only password you remember is the master password for the manager itself. Master password should be a long passphrase, 20+ characters, something like five random words strung together. Good password manager UX makes this easy. Set it up once, you never worry about it again.
The second piece is two-factor authentication. Every major casino operator supports 2FA now. Use it. SMS 2FA is better than nothing but is vulnerable to SIM swapping. App-based 2FA (Google Authenticator, Authy, 1Password's built-in TOTP) is better. Hardware keys (YubiKey) are best but most casinos do not support them yet. If the operator does not offer 2FA at all, that is a signal about their security posture. I would not keep serious money there.
Here is a specific attack vector that does not get enough attention: password reset flows. An attacker who gets into your email account can reset the password on your casino account. So your email account security matters as much as your casino account security. Use a strong unique password and 2FA on your email. If your email is compromised, everything downstream is compromised. Most people focus on the casino password and ignore the email, and the email is the more critical choke point.
The counterargument
The concession I will make is that password fatigue is real. Requiring users to memorize dozens of strong unique passwords is impossible, which is exactly why password managers exist. The mental model of "I have to remember a password" is obsolete. The correct mental model is "my password manager remembers, I remember my master password." Once you make that switch, the friction disappears.
The other concession: no password discipline protects you from a casino that gets breached on the server side. If the operator stores passwords badly and gets hacked, your password could leak regardless of how strong it is. This is why unique passwords matter. Even if your casino password leaks, the attacker cannot use it to log into your other accounts if it is not reused. Unique passwords are a containment strategy against the worst case.
The minimum password I would accept on a casino account: 16 characters, random, generated by a password manager, unique, combined with app-based 2FA, and backed by a strong unique email password with its own 2FA. Anything less and you are a soft target. The effort to set this up is maybe twenty minutes the first time. The cost of getting drained is your full bankroll plus the mental weight of dealing with the operator's dispute process, which can take weeks.
The whole industry would be better off if operators enforced stronger defaults, but they do not, because weak passwords produce higher sign-up rates. So the burden falls on you. Take it seriously. A password you invented in your head for the casino the day you signed up is almost certainly not the password you should be using now. Change it. Use a password manager. Add 2FA. Do the email account too. Then forget about it and go play. Security should be boring, and this is how you make it boring. Anything more exciting than that is a story you do not want to be in.