Device Recognition and Login Alerts at Online Casinos
Device recognition and login alerts are the quietly useful security layer on top of password-and-2FA. Operators do not advertise them much. Here are the claims and the actual mechanics, including the parts that are less flattering to the industry.
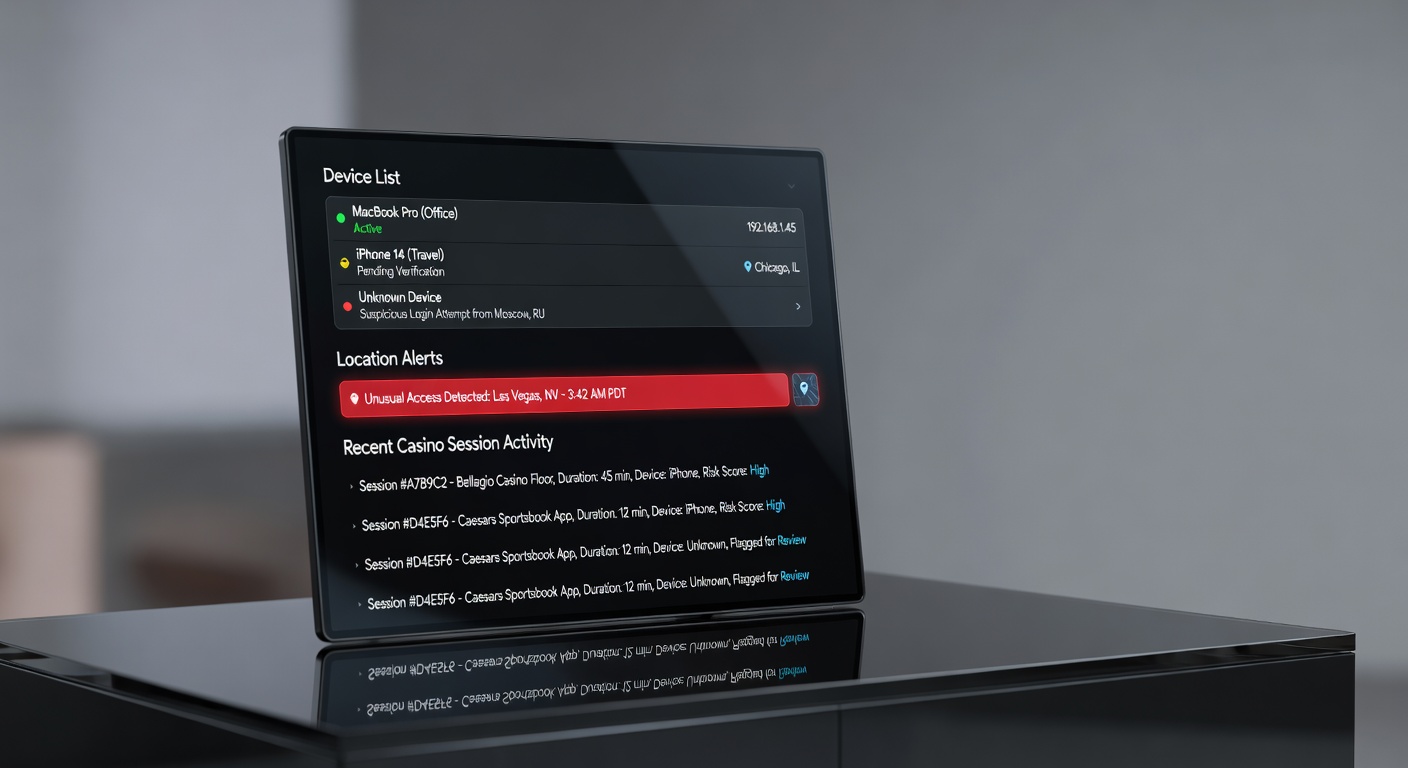
Device recognition is the set of backend systems that identify your browser or app as a known-trusted entity without you doing anything visible. Login alerts are the notifications the casino sends when a new or unusual device accesses your account.
Both are underdiscussed compared to passwords and 2FA. They do a lot of quiet work. They also have failure modes that the marketing copy skips.
Claim 1: Device Fingerprinting Is Just a Cookie
The claim: Device recognition relies on browser cookies. If you clear your cookies, the casino forgets you.
Reality: Modern device fingerprinting is much more sophisticated than cookies. Casino fraud systems use a combination of cookie tokens, browser fingerprint hashes (combining screen resolution, installed fonts, timezone, canvas rendering, WebGL, audio stack), IP address history, and behavioral signals (typing speed, mouse movement patterns). Clearing cookies changes one input. The fingerprint still identifies the device with high probability. This is why casinos can recognize a returning user even after a browser reset or across incognito sessions.
Claim 2: Login Alerts Are a Standard Feature
The claim: All licensed online casinos send an email or push alert when your account is accessed from a new device.
Reality: Not consistently. Licensed operators in the UK and EU generally do send new-device alerts, but implementation varies. Some send alerts on new IP addresses. Some only on new fingerprint hashes. Some only if the login is flagged as suspicious by a fraud scoring model. Some send nothing unless you explicitly enable notifications. The UKGC does not mandate a specific login alert behavior. Operators treat it as a fraud-control feature, not a user-rights feature, which means the alerts are configured for the operator's loss rate, not for your peace of mind.
Claim 3: Unfamiliar Device Alerts Mean Someone Is Trying to Hack You
The claim: If you get a new-device alert you did not trigger, someone is attacking your account.
Reality: Often a false positive. Alerts can fire when you update your browser, switch networks (home wifi to cellular), upgrade your OS, or use a VPN that happens to change your fingerprint in material ways. The signal-to-noise ratio on these alerts is not great. The right response is still to log in and check that no suspicious activity happened, but the alert itself is not reliable evidence of an attack. It is reliable evidence of a change that the fraud system noticed.
Claim 4: The Casino Can See What Else Is on Your Device
The claim: Fingerprinting tells the casino everything about your device: what apps you have, what browsers you use elsewhere, where you are.
Reality: The casino sees what the browser or app exposes via web APIs. That is a meaningful amount of data: your IP, rough geolocation from IP, browser type, OS, screen dimensions, installed fonts (sometimes), audio and graphics capabilities, language settings. It does not include the list of installed applications, your browsing history, or data from other accounts on the same device. The fingerprint is a statistical identifier, not a surveillance dossier. It is still more than most users realize.
Claim 5: A New IP Address Always Triggers a Review
The claim: Logging in from a new IP (hotel wifi, friend's house, coffee shop) triggers a fraud review.
Reality: Sometimes. Modern fraud systems use IP reputation (residential vs datacenter, geographic stability, known-malicious lists) rather than IP novelty alone. A new IP that looks residential and is geographically plausible usually passes without friction. A new IP that looks like a datacenter or VPN often triggers step-up authentication. A new IP that is in a flagged country can trigger an outright block pending review. The IP is one signal among many, weighted by the fraud model. Not all new IPs are treated equally.
Claim 6: Device Recognition Protects Your Balance
The claim: If your device is recognized, withdrawals are fast and automatic. If it is not, withdrawals get held.
Reality: Device recognition does influence withdrawal processing speed at many operators. A withdrawal request from a long-known device with no flags moves through the automated pipeline. A withdrawal request from a new device, especially for a large amount, gets routed to manual review. This is protective in the sense that it catches account takeovers before the funds leave. It is also frustrating in the sense that travelers get their legitimate withdrawals delayed by two to four days.
Claim 7: Operators Share Device Data Across Brands
The claim: If you have an account at one operator, other operators can see your device history through shared data.
Reality: Operators within the same corporate group often share device data internally (Entain's brands, Flutter's brands, MGM's brands). Cross-group data sharing is limited to specific third-party fraud networks like ThreatMetrix, Sift, and Arkose Labs, which collectively see most of the gambling industry's signal. An account takeover attempt at Brand A can be flagged by the fraud network and subsequently block logins at Brand B. The network effects are real. Your bad actor on one site does get remembered on others.
Claim 8: You Can Opt Out of Device Fingerprinting
The claim: Privacy-focused users can opt out of device fingerprinting to protect their privacy.
Reality: In practice, mostly no. Fingerprinting is executed in the browser as part of the account security flow. Opting out would mean the casino cannot run its fraud checks, which means the casino cannot transact with you. Some operators offer reduced fingerprinting for privacy-sensitive users, but it typically comes with manual review on every login and extended withdrawal processing. The privacy-vs-friction tradeoff is not negotiable for most operators. You take the fingerprinting as a cost of service, or you do not have the account.
Device recognition is the backend infrastructure that makes the visible security features actually work. It is imperfect, somewhat invasive, and largely undisclosed. For most users, it is also net-positive for account safety.